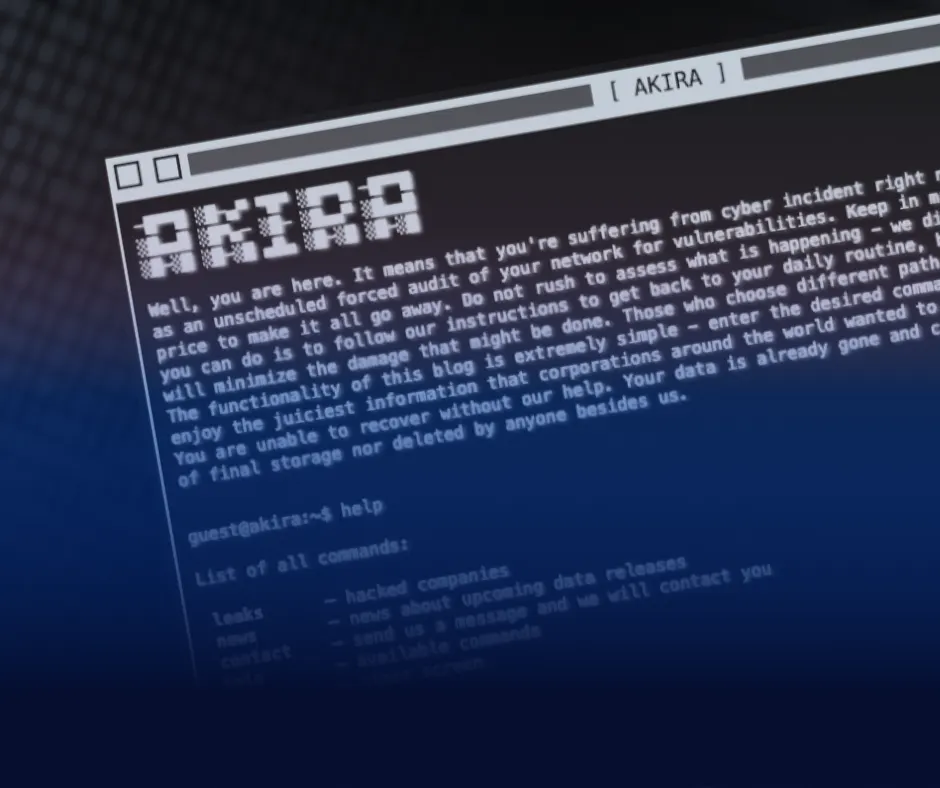
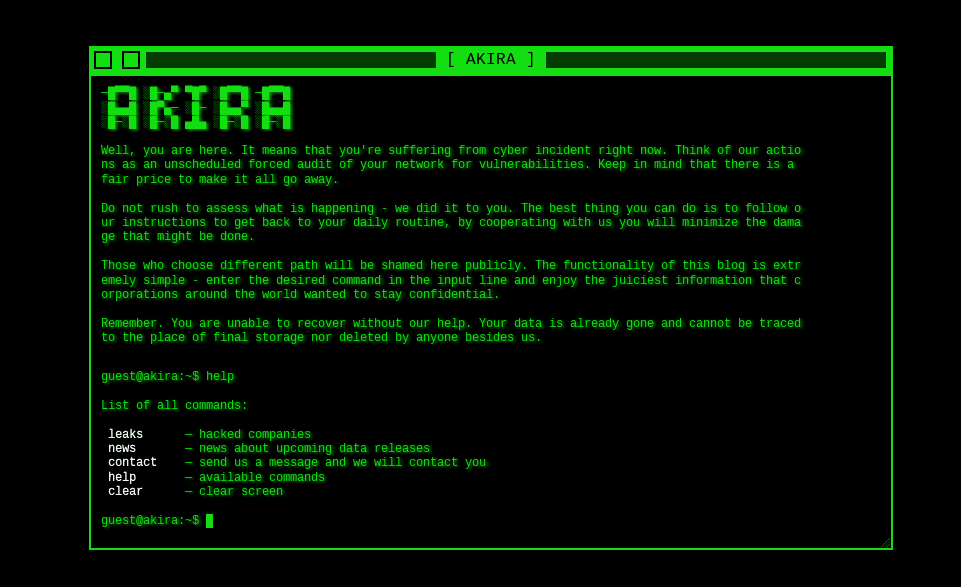
The Akira group uses this style of ransom note to pressure organisations into payment.
Who was targeted
Akira ransomware operators have listed Intellect Systems, a Perth-based operational technology (OT) and engineering provider, on their leak site.
The gang claims to have stolen 10 gigabytes of corporate and personal data, including employee passports, medical files, contracts, and financial information. No samples of the data have been shared, and Intellect Systems has not confirmed the breach as of writing.
Why target Intellect Systems?
Intellect Systems designs and manages OT solutions across Australia and international markets. The company recently became part of Quanta Services, a Fortune 200 contractor involved in energy and pipeline infrastructure. A ransomware breach at this level raises concerns about the exposure of both sensitive employee records and industrial project information.
How Akira is breaking in
The listing comes as Akira increases activity in Australia. The ACSC issued an advisory last week warning that the group is exploiting SonicWall devices.
Akira is also using more than one weakness:
- Devices with unchanged or weak passwords.
- SSLVPN misconfigurations that allow broader access than intended.
- Abuse of the Virtual Office Portal, which in some setups lets attackers configure MFA if they already have valid usernames and passwords.
Together, these gaps give them multiple paths into networks, making it even harder for defenders to block them outright.
What’s at risk
For operational technology firms, the stakes are high. A ransomware breach can also disrupt industrial systems that communities and industries rely on. If Akira follows through with its claim, the data leak could include sensitive designs, contracts and identity documents of staff.
What defenders should do
Australian organisations running SonicWall need to act quickly:
- Apply all available patches, including fixes for CVE-2024-40766.
- Review VPN and portal settings to close off risky configurations.
- Rotate passwords and enforce stronger credential policies.
- Monitor login activity for anomalies that could point to compromise.
Akira’s not stopping here
Akira’s activity in Australia is picking up pace.
The group has been chaining SonicWall flaws to gain persistent access. The alleged breach of Intellect Systems shows us that ransomware gangs are moving into operational technology firms that sit behind energy, pipelines and industrial systems.
These environments are becoming as attractive to attackers as corporate networks, and the impact of a breach here causes the most disruption and chaos out of any industry.