Cyber Security for Healthcare
Increased cybercriminal activity following the pandemic has exposed the healthcare sector, putting compliance, data, and intellectual property protection at risk.

Overview
Malicious actors view healthcare organisations as a profitable target for ransomware and other exploitations. This is due to the sensitive personal and medical data the healthcare sector handles, as well as the importance of this data in managing operations and patient care.
Financially motivated cybercriminals are attempting to gain access to sensitive personal information held by health organisations (such as names, dates of birth, addresses, medical histories, Medicare details, and health fund information) in order to commit identity theft or sell the information in cybercrime marketplaces.
Attacks on hospitals, health trusts, GP offices, and other healthcare entities, as the scope and sophistication of cybercrime grows, have the potential to result in the loss of sensitive patient data and the disruption of important services. Gridware can help you protect your organisation’s data in the even of a breach and meet compliance requirements.
Challenges
Do these challenges sound familiar?
Identifying and responding to security flaws and risks
Identifying vulnerable assets
Balancing information security and system access
Addressing security risks associated with Internet of Things (IoT) devices
Protecting private patient data
Detecting and responding to ransomware

Key Questions
Key security questions for healthcare leaders
In the event of a cyber-attack, how will services be impacted?
Are adequate controls in place to detect and respond to breaches?
Is the personal information of patients properly secured?
In the event of a cyber breach, how would services be impacted?
Are networks and applications examined for vulnerabilities on a regular basis?
Are backups made of systems to prevent data loss in the event of ransomware?
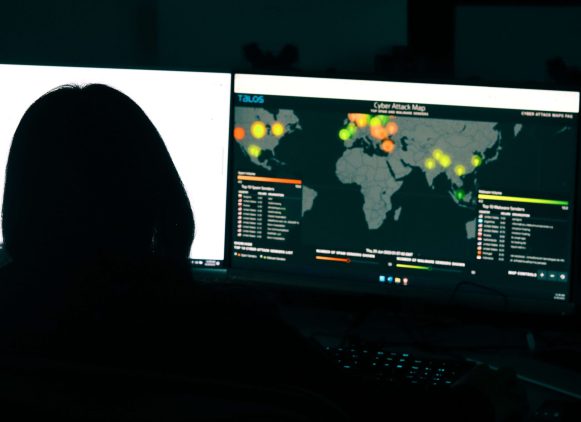
Cyber security compliance in the healthcare industry
As the COVID-19 pandemic continues to have a global impact on the government sector, cybercriminals seek to exploit data and assets relating to vaccine development, treatments, research, and national responses to the COVID-19 outbreak, as this information is now more valuable and prioritised globally.
This abrupt transition has exposed the government industry, placing large risk on compliance as well as data and intellectual property security.
With years of experience collaborating with government organisations, our professionals have a greater understanding of the security and compliance concerns your organisation confronts and how to provide solutions to address them.
Need advice about compliance in healthcare?
Build your defences
Gridware’s Preventative Services
Penetration Testing
PCI DSS Penetration Test
Cloud Security Audit
Network Security Penetration Testing
Cyber Awareness Training
Risk Audit

Gridware's Protective Services
Ransomware Data Recovery
In the event you are subject to ransomware, Gridware’s incident response consultants in can be logged in remotely within minutes to implement our proprietary incident response methodology.
Read Also: why Health care Need Proactive services to stay safe from ransomware attacks
Data Breach Investigation
Read Gridware's Customer Success Stories
Get a Quote
Speak to an Expert Today
Speak to a professional today and get a quote for our penetration testing service.
Insights
Gridware is proud to be a thought-leader in cybersecurity, creating and leading conversations in this space. Check out a selection of our published work from our Sydney based Cyber Defence Centre (CDC), and learn how our cyber expertise has led to partnerships with leading Australian Universities.