Adversary Simulation Exercises

Adversary Simulation Exercises, also known as Red Teaming, are controlled, realistic cybersecurity drills that mimic the tactics, techniques, and procedures (TTPs) of real-world threat actors to test an organization’s detection, response, and containment capabilities. These exercises go beyond traditional penetration tests by focusing on how effectively security teams and controls can identify, respond to, and recover from sophisticated attacks, ultimately strengthening an organization’s overall cyber resilience.

Discover why more organisations trust Gridware for Adversary Simulation to strengthen their cyber resilience. Simulating real-world attacks is one of the most effective ways to test and improve your security before a real breach occurs.

Penetration Testing Services
Adversary Simulation Exercises

Gridware is a leading provider of adversary simulation services to businesses of all sizes - from small medium enterprise to Government and Defence sectors.

Dive deeper into how we’re empowering businesses with superior adversary simulation solutions:

CORIE Framework
Perimeter Assessment
OT/ICS Adversary Simulation
Ransomware Simulation
Password Hash Cracking
XDR/EDR/SIEM Threat Simulation

What is Adversary Simulation?

Adversary Simulation is about testing how well your organisation can stand up to realistic cyberattacks. Unlike a traditional penetration test which focuses on identifying technical vulnerabilities, adversary simulation tailors the full tactics, techniques, and procedures (TTPs) used by real attackers in an environment.

At Gridware, our Adversary Simulation Services are built around your industry, threat landscape, and unique security challenges. We simulate carefully planned attacks to see how your systems, people, and processes respond. Whether it’s defending against cybercriminals, insider threats, or advanced nation-state actors, we help you find and fix the gaps before real attackers can exploit them.

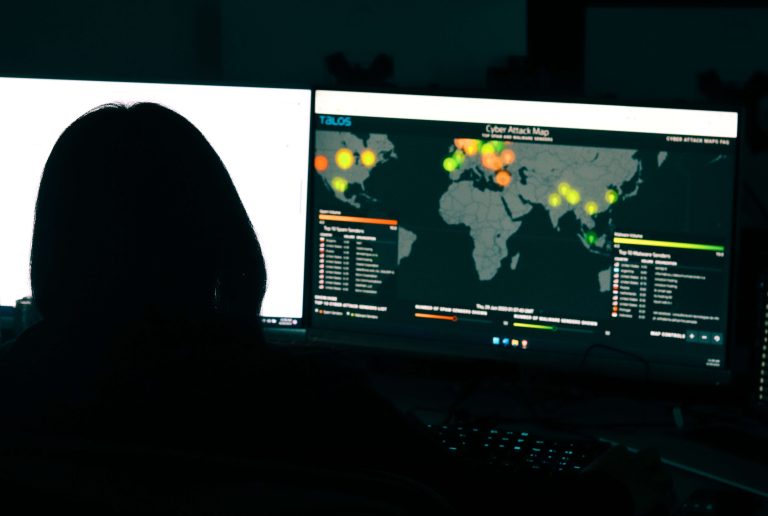
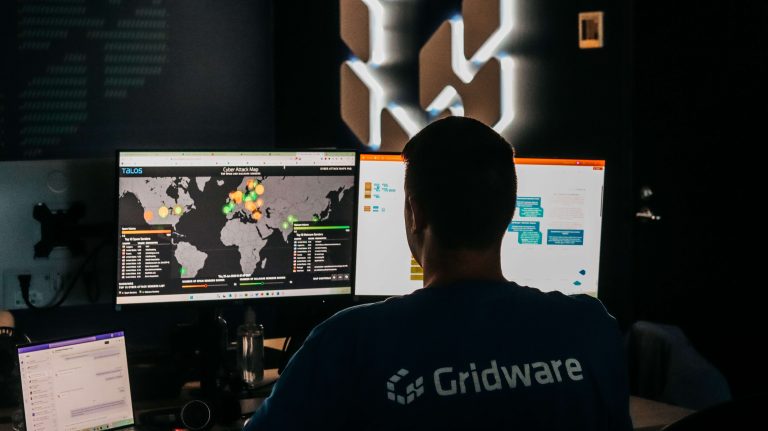
Gridware employee sitting at computer screen looking at world wide cyber threats pointed on a map

Types of Adversary Simulations

We conduct a range of adversary simulation services to emulate attacks in the security of our clients’ IT infrastructure, applications and processes.

Red Teaming

Simulate real-world attacks to test and improve defenses.

Purple Teaming

Enhance existing detection and response capabilities.

CORIE Framework

Assess and fortify security using a structured, threat-based approach.

Physical Perimeter Assessment

Test physical and network defenses against potential breaches.

Reverse Engineering

We analyse threats to uncover vulnerabilities and malicious programming.

OT/ICS Adversary Simulation

Protect critical systems from industrial and operational threats.

Ransomware Simulation

Prepare for ransomware attacks with realistic scenario testing.

XDR/EDR/SIEM Threat Simulation

Strengthen detection and response through advanced simulations.

Gridware is a Best Place to Work 2024 employer

Best adversary simulation providers in Australia

Gridware: Australia’s Leading Experts in Adversary Simulation

As the highest-ranking cybersecurity company in Australia, Gridware takes pride in being certified as a Great Place to Work® and receiving the distinguished Best Workplaces™ award. This makes us not only a leader in cybersecurity but also the Best Cybersecurity Workplace in Australia, demonstrating our unwavering commitment to creating an exceptional work environment.

Our Team Certifications

Gridware’s certification portfolio includes credentials held by both our in-house professionals and our trusted partner consultants.

OSCE3 Certification
OSEP Certification
OSCP Plus Certification
OSCP Certification
OSWP Certification
eWPTX Certification
IRAP
CISM
Hack the box CPTS certification
Certified Red Team professional
Get a Quote
Speak to an Expert Today

Speak to a professional today and get a quote for our adversary simulation service.

Game-Changing

Key Benefits of Adversary Emulation Exercise

Gridware offers penetration testing services that empower organisations to take preventive action against potential downtime, financial loss, and reputational damage. By identifying and addressing vulnerabilities proactively, businesses can stay ahead of the latest cyber security threats.

Experience the Attacker’s Mindset

With our testers across Sydney and Melbourne, our adversary simulation servcices provide a realistic test of your organisation’s ability to defend against actual attack techniques used by cybercriminals. By mimicking real-world tactics, these simulations identify weaknesses in your security posture, offering an unparalleled opportunity to strengthen defenses and safeguard critical assets.

Boost Detection and Response Readiness

These exercises test your security team’s ability to detect and respond to potential intrusions in real-time. By simulating the actions of advanced threat actors, adversary simulation enhances your organisation’s ability to spot malicious activity and respond quickly to mitigate damage.

Pinpoint Your Weakest Links

Adversary simulation identifies and prioritises the gaps in your defenses, whether they’re technical vulnerabilities, process inefficiencies, or human errors. This helps your organisation allocate resources to the areas that matter most.

Stay Ahead of Compliance and Regulation

As cyber threats evolve, regulatory requirements are becoming more stringent. Adversary simulation ensures your security measures align with industry standards and compliance frameworks, demonstrating a proactive approach to protecting data and systems.

The Five Steps for Adversary Simulation Exercise

Objective Setting

We collaborate with you to define the scope, objectives, and parameters of the simulation. This phase ensures the exercise aligns with your organisation’s threat model, critical assets, and compliance requirements.

Boundaries and guidelines are established to ensure the simulation is safe, controlled, and effective. This includes setting expectations for escalation procedures and outlining what is in and out of scope.

Our team conducts reconnaissance to gather information about your systems and processes. Using techniques like OSINT, social engineering, and vulnerability analysis, we identify potential entry points and high-value targets.

We simulate real-world attacker behaviors using tactics, techniques, and procedures (TTPs) aligned with your threat model. This phase tests your systems, people, and processes, exposing weaknesses in your security posture.

After the simulation, we provide a detailed report outlining vulnerabilities, attack paths, and gaps in your defenses. Actionable recommendations are included to help you mitigate risks and strengthen your security framework.

Calculate the cost of your pen test now

Gridware employee sitting in front of a computer screen with cyber threats pointed across a map of the world
Screenshot

Behind the Scenes of adversarial Simulation

Gridware’s adversary simulation services, based in Sydney and Melbourne, bring real-world cyberattacks to life in a controlled environment. Tailored to your organisation’s unique risks, these simulations replicate the tactics of sophisticated threat actors to test your ability to detect, respond, and recover.

By uncovering weaknesses across systems, processes, and people, Gridware provides actionable insights and strategies to strengthen your defences. With adversary simulation, you can stay ahead of evolving cyber threats and build a more resilient organisation.

our clients

At Gridware, we work with a wide range of companies across Sydney, Melbourne, and beyond, delivering tailored adversary simulation services to meet their unique needs. From large enterprises safeguarding critical assets to government agencies navigating strict compliance requirements, our clients trust us to strengthen their cybersecurity posture.

No matter the industry, Gridware’s adversary simulation services empower organisations to build resilience, stay ahead of evolving cyber threats, and protect what matters most.

Kumon
Grimshaw
GBST
redballoon
trendspek
One out of focus computer screen with 2 in focus showing statistics

Why Gridware Leads in Adversary Simulation Services

  • Adversary simulation is a key asset in building a comprehensive and resilient cyber program
  • Gridware is a leader in providing adversary simulation services
  • Gridware follows industry standards and best practices such as OWASP, PTES, OSSTMM, and CREST.
  • Our skilled team utilises a comprehensive range of techniques 
  • By emulating real-world hacker tactics, we ensure that your systems are robust and resilient.
  • Gridware’s unique approach combines proprietary methods with industry best practice standards.
  • Our teams are based in Sydney and Melbourne, serving clients across Australia and Internationally.
  • We have a proven track record of delivering results that protect organizations from financial loss, reputational damage, and lost time.

Frequently Asked Questions About Adversary Simulation

Adversary simulation replicates real-world cyberattacks to test an organisation’s ability to detect, respond, and recover from threats. It involves simulating the tactics, techniques, and procedures (TTPs) used by actual threat actors in a controlled environment.
 

Regular scans will only check and ‘compare’ to data that is often outdated or no longer applicable with the latest developments in the security industry. You need to ‘do as they do’ and perform tests from the perspective of an attacker with the tools attackers utilise to bypass your defences.

Adversary simulation benefits organisations of all sizes and industries, particularly those that handle sensitive data, operate critical infrastructure, or face advanced cyber threats. It’s especially useful for companies looking to improve their detection and response capabilities.

All business applications, even when used in the cloud, are subject to vulnerabilities and exploits. It’s only a matter a time before commonly used applications are compromised and then subsequently patched. We need to check that the patch management process is keeping up with the latest developments, and that they are being patched against exploits. The cloud will only act as a host and cannot guarantee the integrity of any application it hosts.

Not at all. Gridware’s adversary simulations are conducted in a controlled manner to minimise disruption to your operations. Clear rules of engagement are established before the exercise begins. 

With teams in Sydney and Melbourne, Gridware delivers intelligence-led simulations tailored to your organisation’s unique threat landscape. Our experienced professionals replicate real-world attacks to uncover weaknesses, improve defenses, and enhance your overall cybersecurity resilience.

Related Adversary Simulation insights

Gridware Case Study: How we helped fintech leader Astute Wheel

Penetration Testing Case Study: How we assisted social startup Linktree

Gridware Case Study: How we helped education leader Kumon (Web Application Penetration Testing)

Similar services

We partner deeply with clients to understand their needs, working closely and iteratively to provide robust, best-in-class security solutions

Our team is ready to answer to your queries.